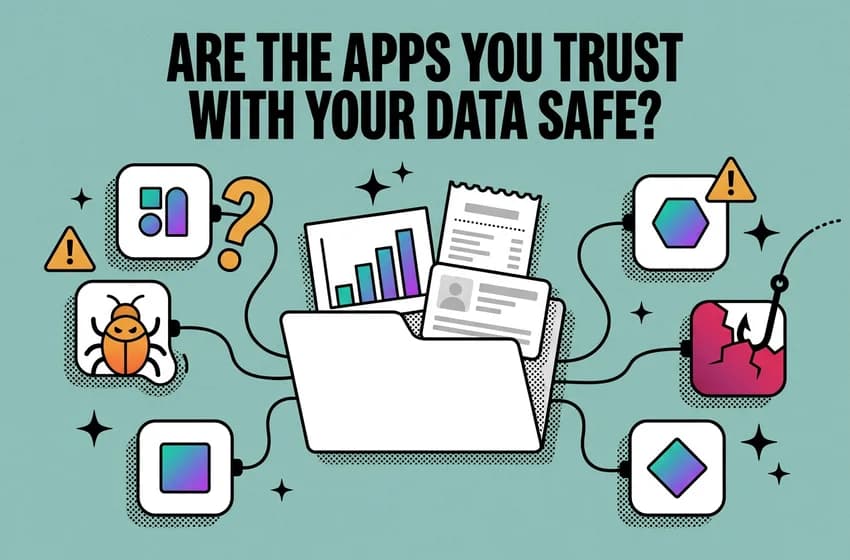
Are the Apps You Trust With Your Store Data Safe? A Shopify App Security Checklist
Table of Contents
- 1. What Happened in the 2026 Shopify Checkout Hijacks
- 2. Why a Trusted App Can Become the Way In
- 3. How to Check Each App's Permissions in Shopify Admin
- 4. How to Check What Apps Add to Your Storefront
- 5. How to Secure Staff Accounts and Sign-In
- 6. Questions to Ask an App Developer Before You Install
- 7. What TrueProfit Does With Your Store Data
- 8. Conclusion
What Happened in the 2026 Shopify Checkout Hijacks
How to Check What Apps Add to Your Storefront
Questions to Ask an App Developer Before You Install
What TrueProfit Does With Your Store Data
Conclusion
Start in Settings > Apps today: open each app's about page, check its unused access, and remove the apps you no longer use. Then check the app embeds in your theme and require two-step authentication for your staff. Shopify's advice is to review app access regularly, so put the next review on your calendar.
I’m part of the TrueProfit content team, but before that, I’m an eCom nerd with 3 years of hands-on experience. I’ve done a bit of everything, but running high-performing ads and making sense of the numbers? That’s my thing. If it’s written here, it’s because I’ve lived it.


I’m part of the TrueProfit content team, but before that, I’m an eCom nerd with 3 years of hands-on experience. I’ve done a bit of everything, but running high-performing ads and making sense of the numbers? That’s my thing. If it’s written here, it’s because I’ve lived it.
 Related readings: